Proxy Connection Reset: Separate Client, Proxy, Target, and Idle Timeout Causes
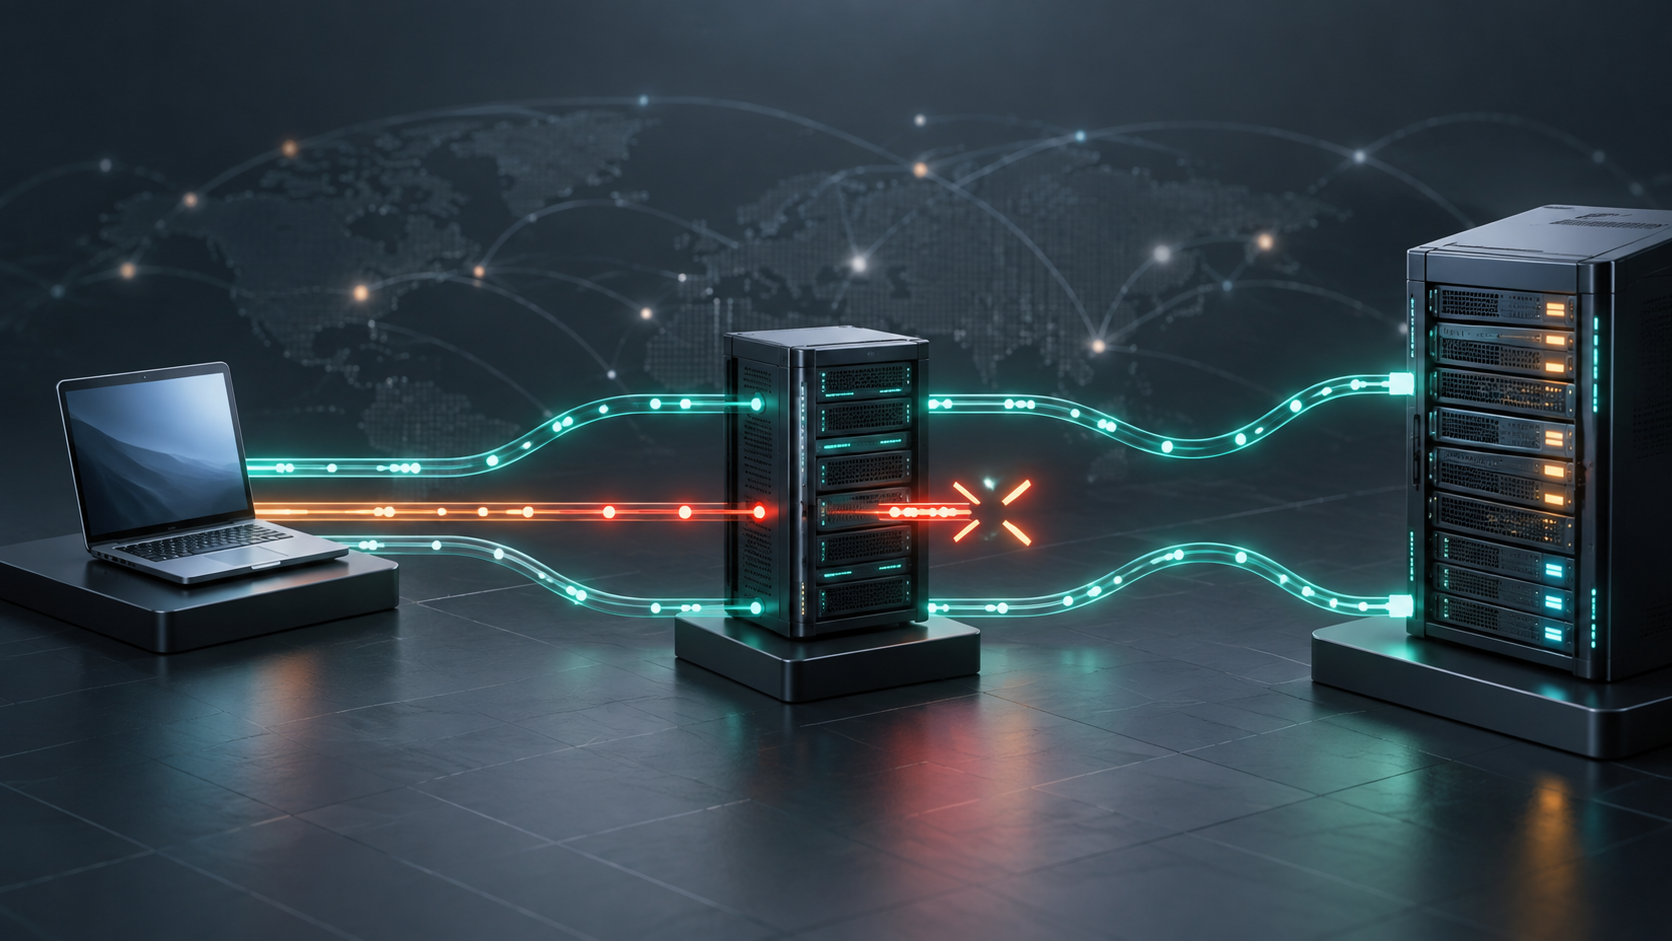
A proxy connection reset means an established TCP connection was closed abruptly instead of ending through a normal exchange. The message may appear as ECONNRESET, connection reset by peer, socket hang up, or a browser network error. Those labels describe the outcome, not the system that sent the reset.
Diagnose the reset in order: locate the request stage, preserve the first error signature, identify which side likely closed the socket, test idle and connection-reuse behavior, and compare one known-good route without changing the client or target. Do not rotate repeatedly before you know whether the reset came from the client, proxy, destination, or an intermediate network device.
Confirm It Is A Reset, Not A Refusal Or Timeout
A refused connection fails while the client is opening a socket. A timeout means a stage exceeded its waiting limit. A reset occurs after a connection exists and one side sends a TCP reset or closes in a way the client reports as abrupt. If no connection was established, start with the connection-refused checks. If the client only reports a deadline, use the timeout stage checks to separate DNS, connect, handshake, and read delays.
Record whether the reset happened before proxy authentication, during an HTTP CONNECT tunnel, during the TLS handshake, while sending the request body, while waiting for response headers, or after a connection sat idle. The stage is usually more useful than the wording of the client error.
Preserve The First Error Signature
Before retrying, record the timestamp, client and version, operating system, proxy protocol, endpoint host and port, exit IP when known, destination hostname, request method, payload size, connection age, and full error text. Also note whether the client reused a pooled connection.
Save the first controlled attempt in the shared troubleshooting log. Repeated retries can rotate the exit, open a fresh socket, trigger rate limits, or move the failure to a different stage. That makes the original reset harder to reproduce.
Use The Reset Stage To Choose The Next Test
| Reset stage | Likely area | Next controlled test |
|---|---|---|
| Immediately after connect | Protocol mismatch, endpoint policy, or intermediary | Verify proxy type, host, port, and authentication method |
| During CONNECT tunneling | Proxy tunnel policy or destination scope | Capture the CONNECT response and test one allowed destination |
| During TLS handshake | SNI, certificate, TLS policy, or route treatment | Follow the TLS-specific comparison path |
| While uploading a request | Payload limit, write timeout, or connection interruption | Repeat with a small low-risk request |
| Before response headers | Destination policy, route quality, or upstream close | Compare the same request through one control exit |
| After an idle period | Idle timeout or stale pooled socket | Disable reuse once and compare connection ages |
If the reset occurs during encryption setup, move to the TLS handshake diagnostics instead of changing generic timeout values. A stage-specific test gives a clearer result than increasing every deadline.
Identify Which Side Closed The Connection
The phrase “by peer” does not always identify the destination server. From the client’s perspective, the peer may be the proxy endpoint. A proxy can also report an upstream close that originated beyond it. Application logs, proxy response codes, connection timing, and provider-side route evidence are safer indicators than the error phrase alone.
Compare four observations: whether the client connected to the proxy, whether proxy authentication completed, whether a tunnel or SOCKS destination request succeeded, and whether any target response bytes arrived. Review the expected HTTP and SOCKS5 behavior because each protocol exposes upstream failures differently.
Test Idle Timeout And Connection Reuse
Connection pools can retain sockets longer than a proxy, load balancer, firewall, or destination allows. The next request then tries to use a socket the other side has already discarded. This often creates a reset on the first request after an idle period while a newly opened connection succeeds.
- Record how long the connection was idle before failure.
- Repeat the same request with connection reuse disabled for one test.
- Compare a fresh connection with a pooled connection using the same route and target.
- Check keep-alive, pool lifetime, and idle-timeout settings at every controlled layer.
- Change one timeout only when the comparison isolates that layer.
Do not make every connection permanent. A pool lifetime shorter than the narrowest known idle timeout is usually easier to reason about than relying on stale-socket retries.
Run One Controlled Route Comparison
- Choose one low-risk destination and one small request.
- Use the same client version, proxy protocol, credentials, and DNS mode.
- Test a fresh connection through a known-good exit.
- Test the suspected exit without changing the request.
- Repeat once with connection reuse enabled and once with a fresh socket.
- Stop when the failure signature is stable enough to assign a layer.
Record latency, exit identity, connection age, reset stage, and response bytes in the proxy health scorecard. If the pool rotates exits between attempts, the result is ambiguous and the comparison must be stabilized before drawing a conclusion.
Classify Pass, Fail, And Ambiguous Results
| Outcome | Evidence | Action |
|---|---|---|
| Client-specific | Another current client succeeds on the same route and target | Inspect client pooling, TLS library, and write behavior |
| Reuse-specific | Fresh sockets pass while aged pooled sockets reset | Align pool lifetime and idle timeout, then retest |
| Target-specific | Other low-risk targets pass through the same route | Review destination scope, request shape, and target policy |
| Exit-specific | Same client and target pass on a control exit but reset on one exit | Quarantine that route and provide the comparison evidence |
| Protocol-specific | HTTP and SOCKS behavior diverge with equivalent settings | Verify tunneling, DNS, and authentication semantics |
| Ambiguous | Exit, target, payload, or client changes between attempts | Stop and reduce the test to one variable |
Know When To Stop
- Stop if the route rotates before the comparison is complete.
- Stop if retries begin producing rate limits or policy responses unrelated to the reset.
- Stop if the test requires weakening certificate validation or destination security.
- Stop if production traffic is affected and a low-risk reproduction is unavailable.
- Stop if client, payload, target, and route are all changing together.
- Stop if provider-side evidence is required to identify an upstream close.
The Practical Diagnostic Order
For a proxy connection reset, first confirm that a socket existed, then locate the reset stage, preserve the initial signature, check whether the connection was reused, and compare the same client and target through one control exit. Classify the result only after the variables stay fixed.
This order prevents a stale pooled socket from being mistaken for a bad IP, a destination policy close from being treated as a generic proxy outage, and repeated rotation from destroying the evidence needed to fix the actual layer.