Proxy TLS Handshake Failure: Separate Certificate, SNI, Protocol, and Route Problems
A proxy TLS handshake failure happens after a network path is reachable but before an encrypted session is ready for normal HTTP traffic. That distinction matters. Replacing the exit IP may not help when the actual cause is certificate validation, server-name routing, TLS version support, or a client that is applying proxy settings at the wrong layer.
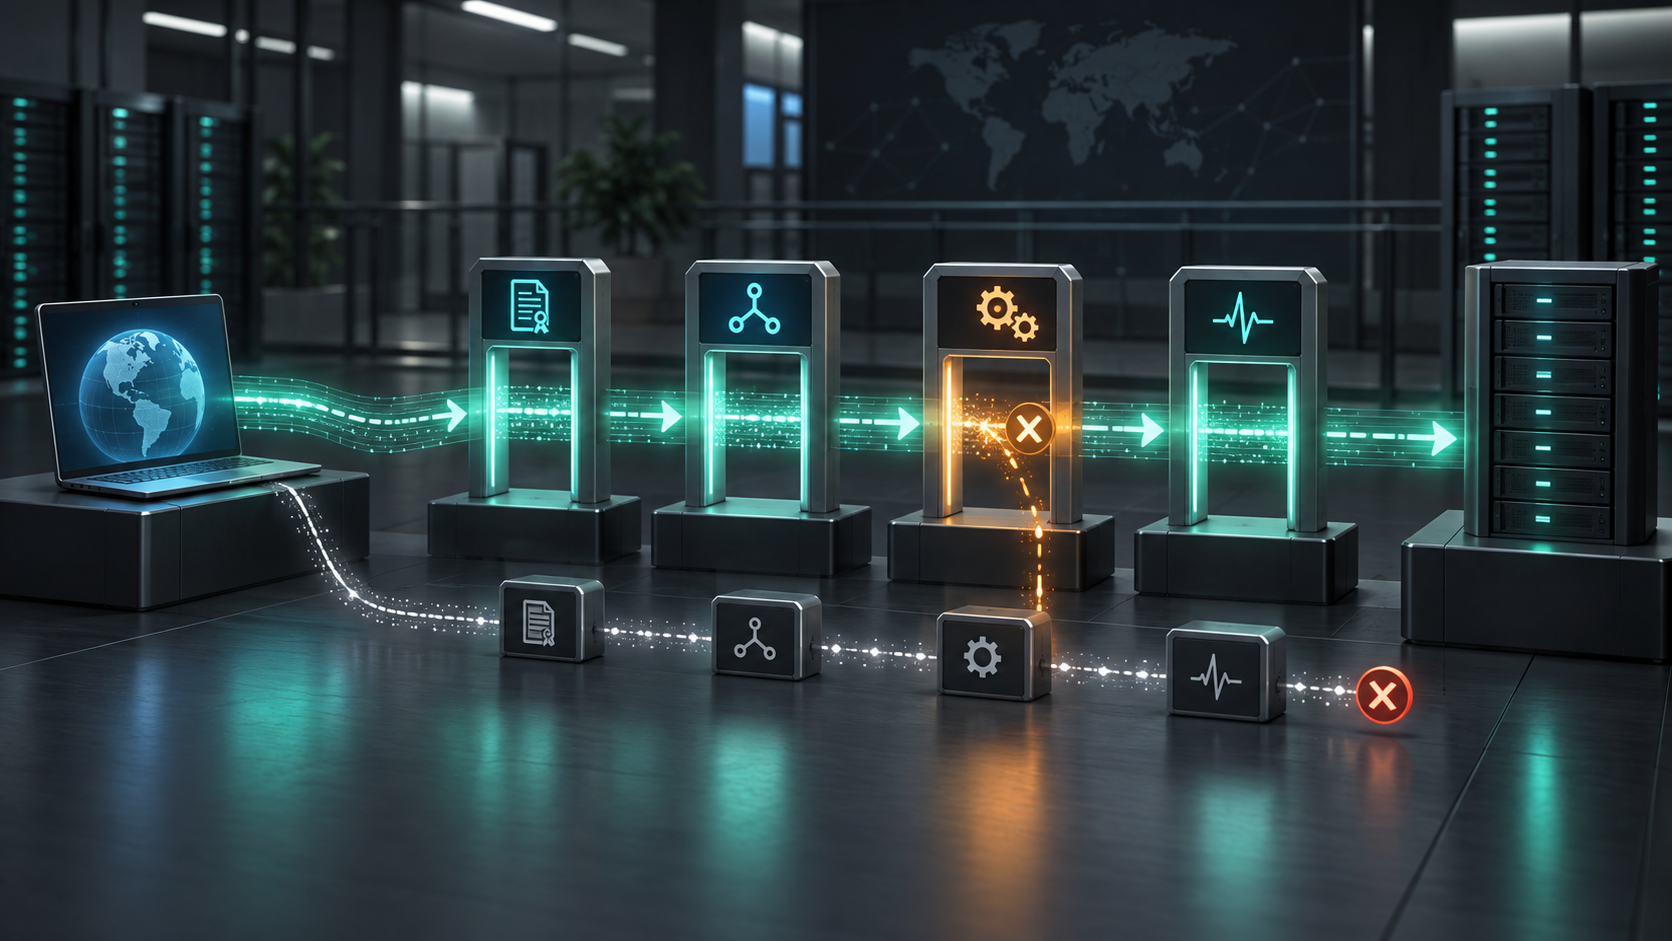
Diagnose the failure in sequence: confirm the transport path, capture the exact TLS error, compare direct and proxied behavior, verify server-name indication, inspect certificate trust, and only then decide whether the exit route is unhealthy. This keeps a handshake problem from being misclassified as a generic timeout or blocked proxy.
Confirm That The Failure Reaches The TLS Stage
First separate a handshake failure from DNS, TCP connect, proxy authentication, and target read delays. A TLS error usually means the client reached a point where encryption parameters or identity validation were exchanged. A connection timeout, refused port, or 407 response belongs to an earlier stage.
Record DNS time, TCP connection result, proxy CONNECT response when applicable, and the first TLS error. The existing timeout stage checks help keep connect and read delays out of the TLS bucket. If the socket never connects, use the connection-refused checks before changing certificate settings.
Capture The Exact Error Before Retrying
Do not reduce every message to “SSL error.” Preserve the client, library version, operating system, target hostname, proxy protocol, exit IP, timestamp, and full error class. Useful distinctions include an untrusted issuer, hostname mismatch, expired certificate, protocol-version rejection, cipher negotiation failure, unexpected connection close, and alert returned by the remote side.
Save one controlled trace in the shared troubleshooting log. Repeated retries can replace the original signal with rate limits, route rotation, or a different exit, making the first failure harder to reproduce.
Use A Failure Matrix To Choose The Next Check
| Observed result | Likely layer | Next controlled check |
|---|---|---|
| TCP connect fails before TLS | Port, firewall, route, or protocol | Verify host, port, proxy type, and reachability |
| Certificate issuer is not trusted | Trust store or interception | Compare certificate chain direct and through the proxy |
| Hostname does not match | SNI, target host, or certificate identity | Retest with the exact hostname and inspect the presented certificate |
| Protocol version alert | TLS policy or old client | Compare supported TLS versions with a current client |
| Handshake closes only on one exit | Route or target treatment | Run the same client and target through a known-good exit |
| Handshake passes but response stalls | Read stage or target behavior | Move diagnosis out of TLS and inspect response timing |
Check SNI And The Target Hostname
Server Name Indication tells a destination which hostname the client expects during the TLS handshake. If a client connects by IP address, sends the wrong hostname, or tunnels through a proxy without preserving the intended target, the destination may present a certificate for another virtual host or reject the handshake.
Retest using the canonical hostname, not a copied destination IP. Confirm that the proxy client sends the target host in the correct CONNECT or SOCKS request and that DNS resolution happens in the intended place. Protocol behavior differs, so compare the documented HTTP and SOCKS5 behavior before treating an SNI symptom as an exit-IP defect.
Compare The Certificate Chain Direct And Through The Proxy
Use a safe diagnostic client to inspect the leaf certificate, issuer chain, validity dates, subject alternative names, and certificate fingerprint. Compare the direct path and proxied path from the same device and network. A different certificate chain can indicate legitimate enterprise inspection, local security software, captive-network behavior, or a misrouted destination. It does not by itself prove malicious interception.
Do not disable certificate verification as a permanent fix. A temporary diagnostic that ignores verification can show whether trust validation is the stopping point, but it removes an important safety check and does not establish that the route is suitable for production.
Verify TLS Version, Cipher, And Client Support
An older runtime may offer protocol versions or cipher suites the target no longer accepts. A strict target may also reject legacy renegotiation or unusual handshake behavior. Compare the failing client with a current command-line or browser client while keeping hostname, proxy, exit, and target constant.
If only one client fails, inspect its TLS library, proxy mode, certificate store, and environment variables. If every client fails through one route but succeeds through a control route, the route deserves deeper isolation. The proxy health scorecard provides a consistent place to record route identity and comparison results.
Run A Controlled Comparison Test
- Choose one target hostname and one low-risk request.
- Use one current client and record its version.
- Test the direct path, if policy allows, and record the certificate chain.
- Test one known-good proxy exit with the same protocol and settings.
- Test the suspected exit without changing credentials, target, or client.
- Repeat only enough times to establish whether the signature is stable.
Before this comparison, confirm the device, browser or client, DNS mode, and exit route through the private proxy setup audit. A test is not controlled when the client silently changes DNS behavior or the pool rotates to another exit between attempts.
Classify Pass, Fail, And Ambiguous Results
| Outcome | Evidence | Action |
|---|---|---|
| Client-specific failure | Current control client passes on the same exit and target | Repair client TLS or trust settings, then retest |
| Target-specific failure | Other targets pass through the same exit | Review target hostname, policy, and TLS requirements |
| Exit-specific failure | Same client and target pass on a control exit but repeatedly fail on the suspected exit | Quarantine the route and compare provider-side evidence |
| Trust-chain failure | Presented chain differs or cannot be built to a trusted root | Identify the presenting system; do not suppress validation |
| Ambiguous | Exit rotates, errors vary, or comparison conditions change | Stop and stabilize the test variables |
Know When To Stop
- Stop if the test requires disabling certificate validation for normal use.
- Stop if the target hostname or SNI value cannot be confirmed.
- Stop if the proxy pool rotates exits during the comparison.
- Stop if repeated requests begin producing rate-limit or policy responses unrelated to TLS.
- Stop if local inspection software or an enterprise trust policy is present but undocumented.
- Stop if changing several variables at once prevents a clear cause from being assigned.
The Practical Diagnostic Order
For a proxy TLS handshake failure, work from the earliest confirmed layer to the latest: transport reachability, proxy authentication and tunneling, target hostname and SNI, certificate identity and trust, TLS version and cipher support, then route-specific comparison. Replace or quarantine an exit only when the same client and target repeatedly succeed on a control exit and fail on the suspected route.
This order protects both security and diagnostic quality. It avoids unsafe certificate workarounds, unnecessary route changes, and retry noise while producing a record another operator can reproduce.