 Rotating Residential Proxies
 Rotating Datacenter Proxies
 Static Residential Proxies
 Static Datacenter Proxies
 Unlimited Rotating Residential Proxies
 Proxy Solutions
 United States Proxies
 Canada Proxies
 United Kingdom Proxies
 France Proxies
 Germany Proxies
 Singapore Proxies
 Japan Proxies
 Australia Proxies
 Vietnam Proxies
 Philippines Proxies
 India Proxies
 Mexico Proxies
 View All Regions
 Social Media
 E-commerce
 Data Aggregation
 Ad Verification
 Artificial Intelligence
 Market Research
 Integration Tools
 Contact Us
 FAQ
 Documentation
 Tutorials
 SDK
 Affiliate Program
 Become an Agent
 Partners
 Blog


Proxy 403 Forbidden: Separate Destination Policy, Route Reputation, and Request Context
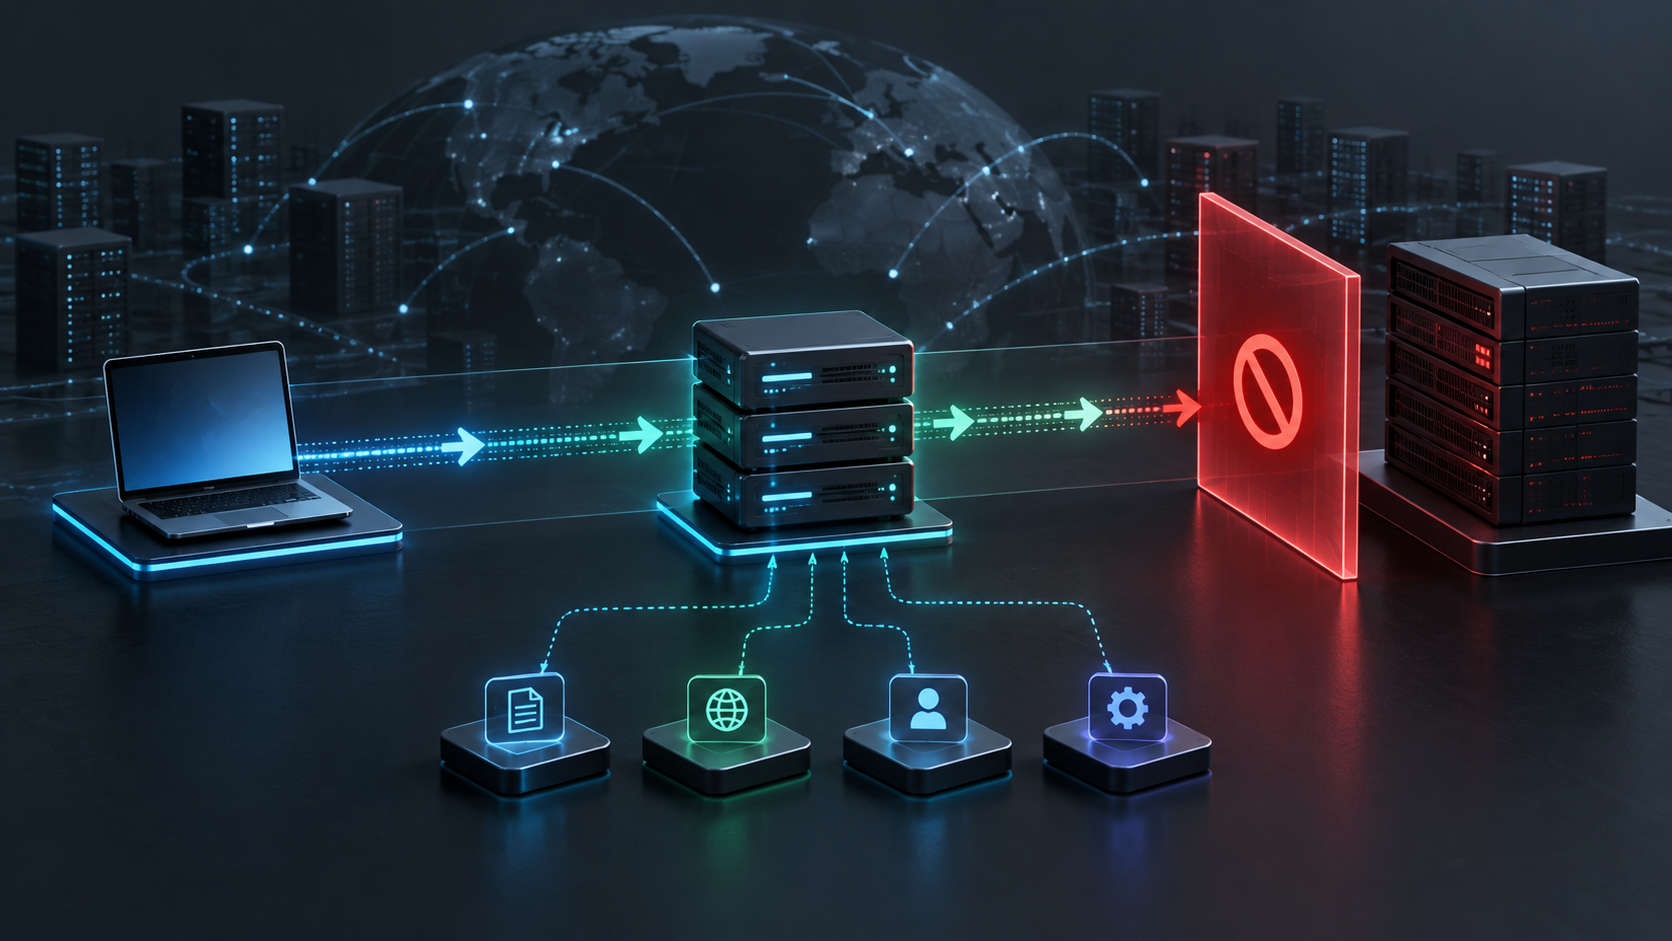
A proxy 403 Forbidden response means an HTTP server understood the request and refused to authorize it. It does not, by itself, prove that the proxy failed. The response can come from the destination application, a CDN or web application firewall, an authentication layer, or a policy gateway between the proxy exit and the origin.
Diagnose it in this order: preserve the first 403 response, identify the likely responder, verify the fixed exit route, compare one approved control request, and classify the result as policy, route reputation, authentication, request context, or ambiguous. Do not rotate repeatedly or modify identity headers to evade an access decision.
Identify Which Layer Returned The 403
| Observed evidence | Likely responder | First record to save |
|---|---|---|
| 403 page uses the destination’s normal layout | Application or origin policy | URL, account state, method, and response signature |
| CDN or edge request ID appears | CDN or web application firewall | Request ID, edge headers, exit IP, and timestamp |
| 403 occurs before the expected application page | Gateway, regional rule, or path policy | Redirect chain, final host, region, and connected address |
| Only an authenticated path returns 403 | Role, entitlement, or session authorization | Signed-in state, resource scope, and account role |
| One exit fails while a control exit passes | Route-specific policy or reputation | Both exit identities and otherwise identical requests |
| Many unrelated destinations return the same page | Proxy-side policy or upstream gateway | Proxy endpoint, response headers, and control targets |
Save the status, response headers, a short body signature, timestamp, destination hostname, request method, proxy endpoint, and exit IP. A branded page or header is useful evidence, but it may be rewritten by an intermediary. Keep the conclusion provisional until a controlled comparison confirms the layer.
Separate 403 From 401, 407, And Transport Failures
A 401 response usually asks the client to authenticate to the destination. A 407 response asks for proxy authentication. A 403 response normally means the responding HTTP layer received enough context to deny access. Timeouts, connection refusals, resets, and TLS alerts are transport failures and require a different diagnostic path.
Confirm that proxy authentication completed and that the 403 is present in the captured HTTP response. If the client substitutes a generic browser message, reproduce with a low-risk diagnostic request that exposes status and headers. Do not label a connection error as a policy denial.
Verify The Exit Route Before Judging Reputation
Record the actual outbound IP, ASN, country or city when relevant, proxy endpoint, session identifier, and test time. Use the exit IP verification process to confirm that the request used the expected route. If the exit changes between tests, the comparison is not stable enough to support a reputation conclusion.
When an account or workflow is assigned to a specific route, compare the observed exit against the route drift checklist. A route mismatch can change region, ASN, and policy context at once, so fix route identity before changing application settings.
Test Destination Policy Without Trying To Evade It
Check whether the requested resource is public, whether the method is allowed, whether the path is correct, and whether the destination documents regional, network, rate, or account restrictions. A successful homepage request does not prove that every API path, login route, or protected resource is permitted.
If the destination explicitly disallows the access pattern, stop. Do not search for a different exit merely to defeat the rule. The safe outcome may be to request authorization, use an approved endpoint, reduce the scope, or discontinue the request.
Compare Route Reputation With Bounded Evidence
Reputation is plausible when one stable exit receives the same 403 across repeated low-risk attempts while an authorized control route reaches the expected response. Check the exit against the IP reputation checks, but do not treat any single blacklist or risk score as definitive proof.
Record the provider, ASN, prefix, prior use where known, destination, and response signature. A route can be accepted by one destination and denied by another. Keep destination-specific policy separate from a broad judgment about the entire proxy pool.
Check Request Context And Header Boundaries
Compare method, path, content type, accepted response type, origin or referrer requirements when documented, and required authentication headers. Use the destination’s published client or API contract as the baseline. Do not add random browser headers, spoof another client, or remove security headers to make the response change.
Inspect whether intermediaries expose or append network metadata using the header exposure audit. The goal is to explain the request path, not to conceal prohibited access. If a trusted boundary is adding an incorrect value, repair that boundary and repeat the same request.
Separate Account Authorization From Network Policy
Run one signed-out request to a public resource and one approved authenticated test to the protected resource. Record account role, entitlement, session age, callback host, and whether the 403 appears before or after authentication. Never import another user’s cookies or credentials for comparison.
If public content passes but a protected path fails across direct and proxied routes, focus on account role or resource authorization. If the same approved session passes directly but fails only through one stable exit, examine route policy, region, and edge selection. Mark the result ambiguous if account state changes between attempts.
Run One Controlled Direct-Versus-Proxy Comparison
- Select one low-risk, authorized request that consistently returns 403.
- Keep the client, destination, method, path, headers, account state, and time window fixed.
- Capture the full response through the suspected proxy exit.
- Repeat through one known-good approved route.
- Where authorized, compare a direct request from the same environment.
- Stop after the smallest comparison identifies a likely layer.
Write the route identity, response signature, and changed variable into the troubleshooting log. Changing the exit, account, user agent, and request headers together produces no reliable diagnosis.
Classify Pass, Fail, Ambiguous, And Stop Outcomes
| Outcome | Evidence | Decision |
|---|---|---|
| Pass | The authorized request reaches its documented response through the expected route | Resume gradually and keep the evidence baseline |
| Destination policy | Direct and proxy paths receive the same documented denial | Request permission, change scope, or stop |
| Route-specific | One fixed exit fails while an approved control route passes | Quarantine the route and escalate with evidence |
| Authorization-specific | Public resources pass but the protected resource fails across routes | Review role, entitlement, and session authorization |
| Ambiguous | Exit, account state, request shape, or response signature changes | Reduce the test to one stable variable |
| Stop | The destination prohibits the access or testing would require evasion | Do not retry through alternate identities or routes |
Retry Only When The Operation Is Safe
A 403 is usually deterministic, so repeated retries rarely repair the underlying decision. Use a small retry budget only when policy state may legitimately be propagating, such as a newly approved allowlist or role update. Follow a bounded retry policy and preserve the same route for the first confirmation.
- Do not replay an uncertain write operation.
- Do not rotate exits to search for one that ignores the rule.
- Do not change account and route in the same test.
- Stop if retries trigger rate limits or broader restrictions.
- Escalate with request IDs and timestamps when provider or destination logs are required.
Keep A Compact 403 Evidence Record
- Timestamp, destination hostname, path, and method
- Proxy endpoint, exit IP, ASN, region, and session identity
- Status, relevant response headers, request ID, and body signature
- Authentication stage, account role, and resource scope
- Direct, suspected-route, and control-route outcomes
- One changed variable and the retest result
- Policy source, stop condition, and escalation owner
The Practical 403 Diagnostic Order
First confirm that the client received an HTTP 403 and identify the likely responder. Next verify the actual exit, preserve the response signature, and compare destination policy, route reputation, request context, and account authorization with one stable control. Classify the result before changing routes or retrying.
This sequence prevents an account-permission failure from being mislabeled as a bad proxy, keeps one destination’s policy from contaminating the whole pool score, and creates an evidence set that supports a safe repair, escalation, or stop decision.