 Rotating Residential Proxies
 Rotating Datacenter Proxies
 Static Residential Proxies
 Static Datacenter Proxies
 Unlimited Rotating Residential Proxies
 Proxy Solutions
 United States Proxies
 Canada Proxies
 United Kingdom Proxies
 France Proxies
 Germany Proxies
 Singapore Proxies
 Japan Proxies
 Australia Proxies
 Vietnam Proxies
 Philippines Proxies
 India Proxies
 Mexico Proxies
 View All Regions
 Social Media
 E-commerce
 Data Aggregation
 Ad Verification
 Artificial Intelligence
 Market Research
 Integration Tools
 Contact Us
 FAQ
 Documentation
 Tutorials
 SDK
 Affiliate Program
 Become an Agent
 Partners
 Blog


Proxy HTTP 408 Request Timeout: Separate Upload Delay, Idle Reuse, and Server Limits
An HTTP 408 Request Timeout means the responding server stopped waiting for the client to finish sending a request. Through a proxy, that can result from a slow upload, a stale keep-alive connection, request-body buffering, a short server deadline, or delay on one route. It is different from a 504, where a gateway times out while waiting for an upstream response.
Preserve the first status, headers, response body, timestamp, request method, payload size, proxy endpoint, and total elapsed time. Keep the destination, request, client, and route fixed while you identify the phase that exceeded its budget. Do not rotate exits, increase every timeout, and repeat a write request at the same time.
Confirm That The Response Is Really HTTP 408
| Observed result | Likely boundary | First evidence to save |
|---|---|---|
| HTTP 408 from the destination or edge | The server stopped waiting for the request | Status, headers, responder signature, method, bytes sent, elapsed time |
| HTTP 504 from a gateway | A gateway stopped waiting for an upstream response | Gateway identity, request ID, and deadline chain |
| Client write timeout | The client could not send data inside its own deadline | Client error, bytes written, socket timing, and upload rate |
| Client read timeout | The client stopped waiting after the request was sent | Request-complete time and time to first response byte |
| Connection reset | A peer closed the connection without a complete HTTP response | Reset phase, connection age, and packet direction |
| Intermittent 408 | Connection reuse, queueing, upload rate, or route latency varies | Matched success and failure samples |
If the tool reports only a generic timeout, capture one low-risk request with a client that exposes the HTTP status and transfer timing. The timeout phase checklist helps separate DNS, connect, TLS, upload, first-byte, and body-read delays.
Identify Who Generated The 408
Inspect server, via, edge, and request-ID headers along with the response-page signature. The responder may be the origin server, a reverse proxy, an API gateway, or an ingress layer. A template or server header is supporting evidence, not proof, because intermediaries can rewrite responses.
Record the final hostname, connected address, redirect chain, proxy endpoint, exit IP, and any trace identifier. If the response is actually a gateway waiting on an upstream service, switch to the 504 gateway deadline guide instead of treating it as a slow client request.
Measure Request Upload Separately From Response Wait
Split the transaction into DNS, TCP connect, proxy authentication or tunnel setup, TLS handshake, request-header upload, request-body upload, time to first response byte, and response transfer. A 408 before the request body finishes points toward upload speed, buffering, body limits, or a server request deadline. A long wait after the request completes points elsewhere.
Record bytes sent at failure, payload size, transfer encoding, content length, and upload duration. A single total time cannot show whether the server waited on headers, body data, or application work.
Compare A Header-Only Request With The Failing Payload
Use one authorized lightweight request to the same destination through the same proxy route. Then repeat the failing method and payload without changing any other variable. If a small request passes but a larger upload reaches the same boundary, investigate body transfer, buffering, and request-size policy before blaming general proxy reachability.
Do not repeatedly submit live writes. Use a documented test endpoint, a dry-run mode, or an idempotency key when available. For a write that may have partially completed, reconcile the operation before another attempt.
Test A Fresh Connection Against Keep-Alive Reuse
A pooled connection can remain open on the client after a server, proxy, or load balancer has expired its idle state. The next request may receive a 408, a reset, or an immediate close. Run one comparison with a fresh connection while keeping the request and route unchanged.
Record connection age, reuse status, idle duration, and which side closed first. If only reused connections fail after a repeatable idle period, align keep-alive limits or retire connections before the shortest boundary. Use the connection reset diagnosis when no complete HTTP response is returned.
Check Expect 100-Continue And Request Buffering
Some clients wait for a 100 Continue response before sending a large body. Some proxies buffer the request before forwarding it, while others stream it. A mismatch can consume the server’s request deadline before useful body bytes arrive.
Capture whether Expect: 100-continue is present, how long the client waits, whether an interim response arrives, and whether the proxy buffers or streams. Change this behavior only in a controlled test and only when the client, proxy, and server documentation support the change.
Map Every Request-Side Deadline
List the client write deadline, proxy request-header and request-body limits, gateway request timeout, server header timeout, server body timeout, and any idle keep-alive limit. The effective boundary is usually the shortest enforced value in the path.
Compare the observed failure time with each configured limit. A failure clustered near 30 seconds is stronger evidence than a single vague timeout message. Do not raise all limits together; longer waits can increase occupied connections and hide a slow-upload or capacity problem.
Run One Stable Route Control
Keep the request and client fixed while comparing the suspected proxy route with one approved control route. Record protocol, endpoint, exit IP, ASN, region, round-trip latency, upload rate, status, and responder signature. Apply the proxy health scorecard to a neutral control destination so route quality is measured independently.
If both routes fail at the same responder boundary, focus on the destination’s request limits or payload behavior. If only one stable route fails and its upload timing is materially worse, quarantine that route and escalate with matched evidence. Do not rotate repeatedly until one attempt happens to pass.
Retry Only When The Operation Is Safe
A 408 can arrive before the server processes a request, but the status alone does not prove that a write had no effect. Query the operation state or use the original idempotency key before retrying a payment, update, submission, or job launch.
- Retry safe reads and known idempotent operations with a small budget.
- Use backoff and jitter rather than immediate parallel attempts.
- Do not retry an uncertain write until its outcome is reconciled.
- Stop when upload latency, error rate, or connection occupancy rises.
- Follow the destination’s published request and rate policies.
Use a bounded retry policy so diagnosis does not become uncontrolled load.
Classify Pass, Fail, Ambiguous, And Stop Outcomes
| Outcome | Evidence | Decision |
|---|---|---|
| Pass | Repeated approved requests complete inside the documented request deadline | Resume gradually and retain the timing baseline |
| Slow upload | Body transfer exceeds the server boundary while small requests pass | Reduce payload or repair the upload path |
| Stale connection | Fresh connections pass while reused connections fail after a stable idle interval | Align keep-alive limits and retire stale connections |
| Server limit | Different stable routes fail at the same responder and deadline | Review request limits with the server owner |
| Route-specific | One fixed route has worse upload timing and repeatable 408 responses | Quarantine the route and escalate with evidence |
| Ambiguous | Payload, route, connection reuse, or responder changes between tests | Reduce the comparison to one variable |
| Stop | The write outcome is uncertain, scope is unauthorized, or retries increase harm | Stop, reconcile, and escalate |
Keep A Compact 408 Evidence Record
- Timestamp, destination, method, payload size, and operation type
- Proxy protocol, endpoint, exit IP, ASN, and expected region
- Status, responder signature, request ID, and response headers
- DNS, connect, TLS, header upload, body upload, first-byte, and total timing
- Bytes sent, upload rate, content length, transfer encoding, and Expect behavior
- Connection age, reuse status, idle duration, and close direction
- Client, proxy, gateway, and server request deadlines
- Fresh-connection, small-request, and stable-route control results
- Idempotency or reconciliation result, owner, and stop condition
Store the evidence in the troubleshooting log. It gives client, proxy, and server owners a shared request timeline instead of reducing every 408 to a generic proxy failure.
The Practical HTTP 408 Diagnostic Order
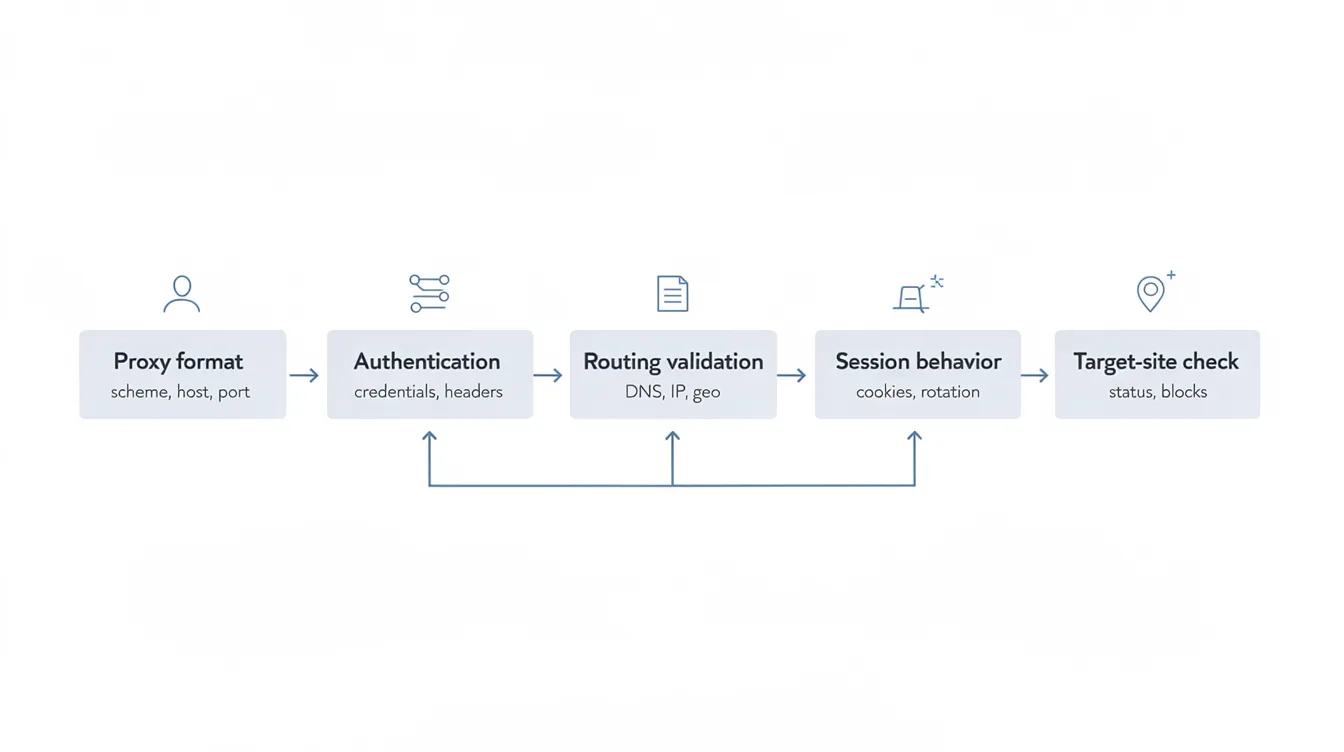
First preserve the HTTP 408 and identify the responder. Then separate upload time from response wait, compare a small request, test a fresh connection, inspect 100-continue and buffering, map request-side deadlines, and run one stable route control. Reconcile uncertain writes before any retry.
This order distinguishes a server request deadline from a 504 gateway deadline, exposes stale connection reuse and slow uploads, and produces a defensible pass, fail, ambiguous, or stop decision without hiding the cause through broad timeout changes or uncontrolled route rotation.