 Rotating Residential Proxies
 Rotating Datacenter Proxies
 Static Residential Proxies
 Static Datacenter Proxies
 Unlimited Rotating Residential Proxies
 Proxy Solutions
 United States Proxies
 Canada Proxies
 United Kingdom Proxies
 France Proxies
 Germany Proxies
 Singapore Proxies
 Japan Proxies
 Australia Proxies
 Vietnam Proxies
 Philippines Proxies
 India Proxies
 Mexico Proxies
 View All Regions
 Social Media
 E-commerce
 Data Aggregation
 Ad Verification
 Artificial Intelligence
 Market Research
 Integration Tools
 Contact Us
 FAQ
 Documentation
 Tutorials
 SDK
 Affiliate Program
 Become an Agent
 Partners
 Blog


Proxy HTTP 431 Request Header Fields Too Large: Trace Cookies, Forwarding Chains, and Gateway Limits
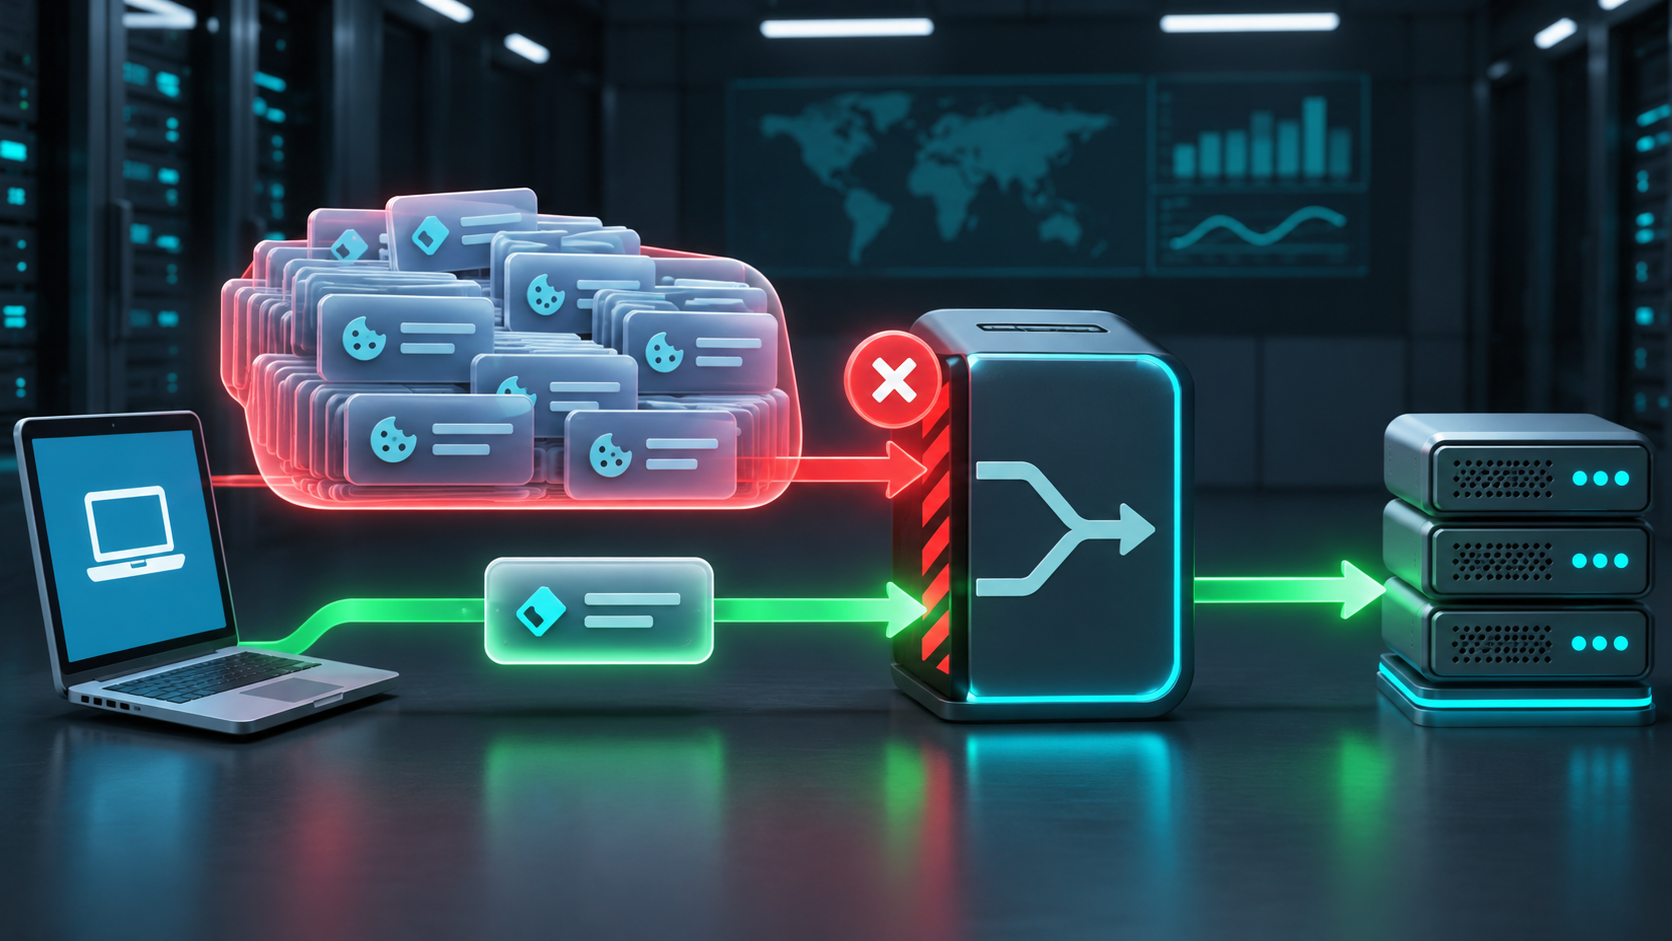
HTTP 431 Request Header Fields Too Large means a server or gateway rejected the request-header section before it could process the request normally. Through a proxy route, the excess may come from one large Cookie or Authorization field, too many accumulated cookies, repeated forwarding headers, or a lower header limit at an intermediary. It does not prove that the exit IP is blocked.
Preserve one failed request before deleting state or rotating routes. Record the final URL, method, total request-header bytes, the largest fields by byte count, cookie count, redirect chain, proxy endpoint, exit IP, response headers, and timestamp. Use only approved test accounts and redact secret values; header names and byte lengths are usually enough for diagnosis.
Classify The 431 Before Changing The Proxy
| Observation | Leading branch | Next controlled check |
|---|---|---|
| Direct and proxy requests both return 431 | Client state or origin limit | Measure fields and test a clean approved session |
| Direct works but the proxy path returns 431 | Intermediary limit or added forwarding fields | Compare the transmitted header set at each path |
| 431 appears after redirects | Cookie growth or host transition | Disable automatic redirects and inspect each hop |
| Only one browser profile fails | Stored cookies or extensions | Compare profile state without copying credentials |
| Failure changes by gateway | Per-hop header limit | Hold the request constant and identify the rejecting hop |
1. Confirm That The Response Is Really HTTP 431
Capture the status line, Server, Via, request identifier, and safe body signature. A client-side error, proxy authentication failure, or HTTP 413 body-size rejection belongs to a different branch. Use the HTTP 413 size-limit guide when the request body, rather than the header section, is oversized.
2. Measure Header Bytes Instead Of Counting Lines
Calculate bytes after serialization, including field names, separators, delimiters, and character encoding. Record total bytes and the top five fields by size. One long Cookie field can dominate the request, while many small fields can exceed a count or aggregate limit. Do not place secret values in the troubleshooting record.
3. Find Cookie Growth By Domain And Path
List cookie names, domains, paths, expiry state, and byte lengths without exposing values. Redirects between subdomains can cause several valid cookie sets to travel together. A pass is a bounded cookie set that remains stable across two identical requests. A fail is repeatable growth or duplicated names. An ambiguous result requires the application owner to confirm expected cookie scope.
4. Compare One Fixed Direct And Proxy Request
Keep the client, URL, method, session, and redirect behavior unchanged. Send one direct request and one through a fixed proxy endpoint, then compare header names and byte counts. If the proxy path adds or repeats forwarding fields, use the proxy header exposure check to separate expected metadata from unintended duplication.
5. Inspect Forwarding Chains For Repeated Fields
Check Forwarded, X-Forwarded-For, Via, trace identifiers, and vendor-specific routing fields. Multiple intermediaries may append values, but the same hop should not duplicate the whole chain on every retry. Stop if changing these fields would bypass an access or audit policy; the gateway owner must correct that configuration.
6. Separate Authorization Size From Authentication Failure
Measure the Authorization field and any signed metadata without recording the credential. A large token can trigger 431, while an invalid proxy credential more often produces 407. Follow the proxy authentication checklist when credentials, allowlists, or authentication scope are the actual failure.
7. Trace Redirects One Hop At A Time
Disable automatic redirects and record each status, Location target, host, Set-Cookie names, and next-request header bytes. A redirect can move the request to a host with a lower limit or add cookies before the final request. Do not forward Authorization or cookies to a different host unless the service contract explicitly requires it.
8. Compare Browser And Scripted Clients Carefully
A browser may add cookies, client hints, extension headers, and cached authentication state that a minimal script does not send. Compare field names and byte sizes rather than assuming the clients are equivalent. If one stored account context alone fails, the session mismatch guide helps separate route identity from local session state.
9. Locate The Enforcing Hop
Compare response markers, timing, request identifiers, and documented limits for the client library, forward proxy, edge gateway, reverse proxy, and origin. Do not raise every limit at once. A higher limit at the first gateway can simply move the rejection downstream or increase memory pressure.
10. Run A Minimal Approved Control
When policy permits, use a clean test account or a new approved session with the same URL and fixed proxy. Do not copy production cookies into the control. If the clean control works and the stored session fails, cookie or profile state is the leading branch. If both fail at the same byte threshold, investigate the enforcing limit.
Pass, Fail, Ambiguous, And Stop Conditions
| Result | Decision | Action |
|---|---|---|
| Reduced approved headers pass on both paths | Pass | Correct the field source and restore traffic gradually |
| Same threshold fails direct and proxied | Origin or shared gateway limit | Escalate with byte measurements |
| Proxy path adds repeated forwarding fields | Intermediary configuration | Stop rotation and repair the responsible hop |
| Only stored browser state fails | Session-state branch | Review cookie scope and approved reset procedure |
| Secret values, ownership, or request state are unclear | Stop | Redact evidence and involve the service owner |
11. Change The Route Only When The Evidence Points There
A route comparison is justified only when the request is fixed, direct access succeeds, and one proxy gateway repeatedly rejects the same header set at a different threshold. Use private proxy routes to test one comparable endpoint while changing only the route. Broad rotation destroys the comparison.
12. Keep A Compact 431 Evidence Record
Save the timestamp, client, URL, method, redirect hop, total header bytes, largest field names and sizes, cookie count, proxy endpoint, exit IP, response owner, request identifier, direct result, proxied result, and final decision. The troubleshooting log provides a reusable handoff format.
Use Header Evidence Before Raising Limits
A reliable 431 workflow is: confirm the responder, measure serialized headers, identify cookie or forwarding growth, compare one fixed direct/proxy pair, trace redirects, locate the enforcing hop, and run one bounded control. Remove only unnecessary approved fields or correct their scope; raise a limit only with the owning team and a documented operational reason.